Most privacy and security guides focus on one piece—passwords, apps, or settings—then leave you to stitch it all together. That’s a problem, because real risk comes from how many small choices interact: what you store, what you share, who you trust, and whether your devices and accounts are prepared for mistakes.
This supporting guide from andyday.tv is built around one practical long-tail goal: applying privacy, security, and legal safety best practices to your daily online accounts without creating extra friction. You’ll get concrete checklists, decision rules, and safer defaults you can implement step by step.
Start With Threat Modeling That Fits Real Life (Not a Fantasy)
Before you change settings, decide what you’re protecting against. For most people, the most realistic threats are account takeover from weak credentials, phishing-driven credential theft, accidental oversharing through social or messaging apps, and legal trouble from storing or transmitting sensitive content without proper permission.
A simple, usable approach is to write down three scenarios you want to prevent. For example: “Someone logs into my email,” “I accidentally publish personal or sensitive information,” and “I share content I’m not allowed to share.” Then you choose controls that directly reduce those risks.
This matters because security measures aren’t one-size-fits-all. If your biggest risk is account takeover, prioritizing password and authentication controls will beat installing many apps. If oversharing is your risk, you’ll benefit more from privacy settings and data minimization than from complex tooling.
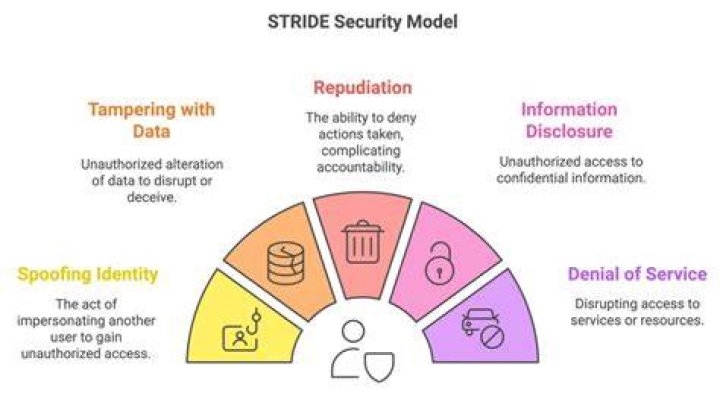
Threat modeling doesn’t need to be technical. It needs to be specific enough that your next steps actually address your risk.
Lock Down Account Access With the “Minimum Necessary” Standard
Account protection is the center of gravity for privacy and security. If someone can access your email, social accounts, cloud storage, or payment methods, they can often reset passwords for everything else. That’s why your first priority should be strong authentication and reducing where attackers can reach you.
Use a password manager if you can. Unique passwords for each account reduce the blast radius when one service is breached. Next, enable multi-factor authentication (MFA) on your most important accounts—email first, then banking and any account that can reset other passwords.
When choosing MFA methods, prioritize options resistant to interception. Authenticator apps or security keys generally provide stronger protection than SMS in many threat scenarios. If you must use SMS, treat it as a fallback and keep your phone account secured as well.
Adopt a Practical Password Hygiene Routine
Good password hygiene is not just “use a complex password.” It’s about consistency and avoiding predictable patterns. Create passwords that are unique, long enough, and generated by a manager rather than improvised from personal facts.
Also reduce account recovery risk. Review recovery emails, phone numbers, and trusted devices. Attackers frequently regain access through recovery flows, so cleaning up recovery options is a meaningful legal safety and privacy step, not just a security one.
- Change passwords only where you suspect risk or where you have weak credentials.
- Remove old recovery methods you no longer control.
- Review logged-in sessions and revoke access you don’t recognize.
Phishing Defense: Reduce Clicks, Verify Requests, and Expect Social Engineering
Phishing works because it blends into normal life: “reset your password,” “confirm your shipment,” “verify your account,” or “security alert.” Most phishing campaigns aim for credentials first and data later. For privacy and legal safety, the goal is to prevent your accounts from being used to take over others or to send harmful content under your identity.
Use a “pause and verify” rule for any login request, account warning, or message requesting payment or documents. Instead of clicking links in messages, open the service directly by typing the address yourself or using a trusted bookmark you created.
Be especially cautious with attachments and document links. Many legal and compliance issues start when you accept a file you shouldn’t open or share information from it without understanding what it contains.
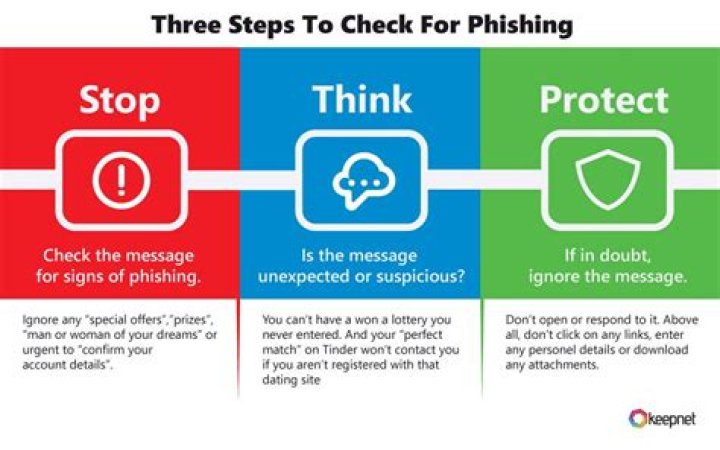
Phishing defense is mostly habits: slow down, verify the sender, and access services through trusted paths.
Create a Verification Script You Can Reuse
When you receive a suspicious request, use a short checklist. Check whether the message matches your expectations, confirm via another channel, and avoid entering credentials on pages you didn’t navigate to intentionally.
If the message claims urgency, treat that as a red flag. Attackers frequently pressure people to skip verification.
- Does the sender address look right, including domain and formatting?
- Does the message ask for credentials, codes, or unusual payment instructions?
- Can you verify the claim by opening the service directly?
- Would you ask a colleague or use a known contact method to confirm?
Secure Your Devices and Browsers: The Front Door for Privacy
Your browser is where many privacy and security decisions happen. It stores session states, loads content from the web, and can retain sensitive data like form inputs. If the device is compromised, account protections won’t save you—attackers can still capture passwords, cookies, or session tokens.
Keep your operating system and browser updated. Updates often address security vulnerabilities that actively enable compromise. Also review installed extensions and remove anything you don’t trust or don’t need.
Finally, consider device-level protections like full-disk encryption where supported, plus a strong screen lock. These controls matter for legal safety too because a lost device can expose data that you may be required to protect under certain privacy or workplace policies.
Make Cookie and Session Management Work for You
Cookies and sessions make services convenient, but they also extend risk if stolen. Use logout practices when sharing a device, and regularly review browser settings for “remember me” sessions. If you use multiple accounts, consider separate browser profiles to reduce accidental cross-account mixing.
For high-sensitivity tasks, prefer private browsing only as a privacy feature for that session, not as a complete protection model. Private mode can still be vulnerable depending on device security and how websites and extensions behave.
- Remove unnecessary browser extensions.
- Use a strong device lock and encryption when available.
- Review saved passwords only if you control the device environment.
Practice Data Minimization: Share Less to Risk Less
Privacy isn’t only about hiding—it’s also about storing less. Data minimization reduces the amount of personal information attackers can steal, and it lowers the likelihood you accidentally share something that creates legal consequences. Many legal safety issues arise when people upload documents or personal identifiers to the wrong place, or share content without understanding retention and access.
Adopt the rule of collecting the minimum required and sharing only what’s necessary. Before you post, upload, or send a file, ask: Who else could access this? How long might it be retained? Can you share a less sensitive version instead?
Sharing less reduces both technical exposure and legal risk from unintended disclosure.
Use Safer Sharing Defaults for Social and Messaging Apps
Social platforms and messaging apps vary, but they commonly include privacy controls like audience selection, profile visibility, and metadata handling. Set visibility to the narrowest audience that meets your goal. If you don’t need it public, don’t make it public.
Also check whether apps include location tags, read receipts, or automatically shared contact information. Those details can turn a normal message into a dataset that’s useful to attackers.
- Prefer “friends only” or smaller audiences when possible.
- Disable location tagging if it’s not required.
- Review who can message you and who can see your posts.
Legal Safety Basics for Privacy-Conscious People
Legal safety overlaps with security in a simple way: actions that create privacy harm can also create legal exposure. That includes sharing content you don’t have rights to, uploading documents without permission, or collecting personal data about others without consent where required. Even when laws vary by jurisdiction, the responsible approach is consistent—protect sensitive information and control how it’s shared.
Start by treating “sensitive information” as a category, not a single file. This includes personal identifiers, financial details, health-related information, credentials, private messages, and any documents that reveal private relationships or obligations.
When you share a document, check for hidden information. Many files include metadata like author names, device identifiers, and revision history. Before uploading or forwarding, remove unnecessary metadata and confirm you’re not exposing sensitive pages.
A Simple “Permission and Purpose” Rule for Sharing Content
Use a permission and purpose check before you transmit anything sensitive or potentially copyrighted. Ask whether you have permission to share the content and whether your purpose is legitimate and necessary. If either answer is unclear, use a safer alternative such as sharing a summary instead of the file.
Be careful with screenshots. Screenshots can preserve more context than you intended, including usernames, email addresses, and notifications.
- Verify you have rights or permission before sharing content.
- Share only what’s needed for the purpose.
- Remove metadata and cover identifiers in screenshots.
Respond Faster: Have an Incident Plan Before You Need One
Even with good habits, breaches and mistakes can happen. Having a quick response plan reduces harm and improves your chances of limiting damage. Your goal is to stop further access, preserve evidence, and notify relevant parties when appropriate.
If you suspect account compromise, act in this order: change passwords, secure MFA, revoke active sessions, and review recovery methods. Then check other connected accounts because attackers often pivot through email and authentication flows.
Document what happened. Keep timestamps, screenshots of suspicious messages, and any relevant emails. This supports troubleshooting and can be important for legal or support workflows when you contact providers or determine next steps.
Know When to Contact Support and When to Escalate
If you detect credential theft or unauthorized access, contact the relevant service quickly. Many platforms provide recovery options and can help trace unusual login activity. If financial transactions are involved, you may need to contact your bank or payment provider immediately to limit losses.
Remember that urgency doesn’t mean guessing. Secure your accounts first, then escalate using official support channels.
- Secure email and authentication paths first.
- Revoke sessions and review account activity logs.
- Use official support portals and never rely on suspicious links.
How andyday.tv Fits Into a Safer Privacy and Security Routine
Security and privacy are ongoing practices, not one-time settings. That’s where andyday.tv can help as a supporting resource: it encourages practical, human-first improvements so you don’t just “learn security,” but apply it consistently to your everyday accounts and sharing habits.
Use this guide as your baseline, then build a routine that’s easy to maintain. For example: update devices monthly, review account recovery options quarterly, and revisit privacy settings when platforms change features.
When you treat privacy and security as a process, you reduce the likelihood of mistakes—and you also reduce the odds that those mistakes create legal safety issues.
Final Thoughts
Privacy, security, and legal safety aren’t separate topics for most people—they’re interconnected outcomes of daily account hygiene, sharing decisions, and device protection. Start with practical access controls, defend against phishing with verification habits, minimize data exposure, and apply a permission-and-purpose rule before sharing sensitive content. With a consistent routine, and andyday.tv as a supporting reference, you can make your online presence safer without turning life into a checklist.
