When you use streaming and entertainment websites, privacy, legal safety, and account security are tightly connected. The choices you make—what you sign up for, how you handle passwords, what you install, and how you browse—can meaningfully reduce risk. This guide focuses on one practical long-tail goal: how to use kissasian with stronger privacy and better account protection, without turning your device into a weak link.
Because many users look up “is it safe,” “how do I protect my account,” or “how can I stay private,” this article emphasizes the exact behaviors that matter day to day. If you follow the checklist-style guidance below, you’ll be in a better position to prevent common account takeovers, reduce tracking, and avoid avoidable legal and safety problems.
Clarify Your Threat Model Before You Change Anything
Before you adjust settings, it helps to name what you’re protecting against. Most risks fall into a few categories: account takeover (credential theft), privacy loss (tracking and profiling), malware exposure (unsafe downloads or malicious redirects), and payment risk (fraudulent charges). Once you know which of these you care about most, you can prioritize the most effective controls.
For kissasian users, the most common practical concerns are usually account security and privacy. That means you should focus on protecting login credentials, limiting how much personal data you expose, and keeping your devices free from risky software. Start with the basics, then layer protections only where they provide clear benefits.
Use Strong, Unique Passwords With a Password Manager
Weak or reused passwords are one of the fastest paths to account compromise. If attackers obtain credentials from any other site through phishing or data breaches, password reuse can lead to “credential stuffing,” where the same login is tested across many services. The most reliable defense is using a unique, high-entropy password for each account you have.
A password manager reduces friction and makes unique passwords realistic. Instead of remembering complex strings, the manager stores them securely and fills them when you need to log in. When you set up your kissasian account, avoid reusing older passwords and generate a new one dedicated to that account.
Also review your email security, because account recovery usually runs through your inbox. If your email password is weak, strong passwords elsewhere won’t fully protect you. Treat your email account as the “master key,” and harden it first.
Turn On Two-Factor Authentication and Confirm Your Recovery Options
Two-factor authentication (2FA) adds a second barrier after your password. Even if someone steals your password, they still need the second factor to sign in. Whenever kissasian supports 2FA, enable it and prefer an authenticator app over SMS when possible.
SMS can be vulnerable to SIM swapping and number porting attacks, depending on your carrier and local threat conditions. Authenticator apps generally provide stronger protection because they generate time-based codes locally on your device. After enabling 2FA, don’t stop there—confirm your backup codes and save them safely.
Recovery options matter just as much as login protection. Check whether your account recovery method uses email, phone number, or other identity steps. If you changed phones recently or still have old numbers linked, update them to reduce recovery risk.
Minimize Personal Data You Share During Sign-Up
Privacy begins before you ever log in. Many accounts request optional profile fields; if you don’t need them, choose the least identifying setup. Avoid using the same display name or username you use on other platforms if you care about reducing cross-site correlation.
When possible, use only the minimum details required for an account. Also be cautious with “one-click” profile features that may import data from social accounts. Those integrations can expose more information than you expect, including lists of connections, email metadata, or device identifiers.
Finally, review whether the platform allows you to adjust visibility, marketing preferences, or data sharing. Even small toggles can reduce unwanted tracking and keep your inbox cleaner.
Reduce Browser Fingerprinting and Tracking Signals
Even if you avoid risky downloads, websites can still track usage patterns. Tracking may include cookies, device fingerprints, and analytics identifiers. You can reduce exposure by using privacy-respecting browser settings, limiting third-party cookies, and controlling permissions like location or notifications.
Focus on the highest-impact controls first. Clear unnecessary site data periodically, disable permission prompts you don’t use, and keep your browser updated. Also consider using a reputable privacy-focused browser configuration or extension set that limits cross-site tracking and blocks known trackers.
When you visit kissasian pages, avoid staying logged in on shared or public devices. If you frequently watch on different devices, use “sign out” when you’re done and keep separate sessions for separate devices when that’s available.
Verify Site Authenticity and Avoid Suspicious Links
Not every “kissasian” link you find is necessarily legitimate. Attackers may use look-alike domains, misleading redirects, or ads that send you to impersonation pages. Before you enter credentials, confirm that the site uses the expected secure connection behavior for modern browsers and that the address looks correct.
A practical rule: never log in from a link inside a random email, a message you weren’t expecting, or a pop-up that claims you must act immediately. If you want to log in, type the address yourself or use a trusted bookmark. That reduces the chance you land on a phishing page designed to steal your password.
Also watch for unusual prompts requesting excessive permissions, unexpected downloads, or “captcha loops” that repeat after you complete them. These can be indicators of tampering or malicious injection.
Protect Your Device From Malware and “Drive-By” Risk
Your login security depends on your device health. Malware can steal saved passwords, intercept keystrokes, and redirect you to malicious pages. The simplest defenses are also the most effective: keep your operating system updated, use reputable anti-malware tools, and avoid installing “helper” software from unknown sources.
Be especially cautious with browser extensions. A single malicious extension can read and manipulate web content or capture session tokens. Only install extensions you truly need, review permissions carefully, and remove anything you no longer use.
If you ever notice sudden pop-ups, unexpected browser redirects, or changes in your homepage or search engine, investigate immediately. Reset your browser settings, scan the device, and change passwords after you’ve removed the cause.
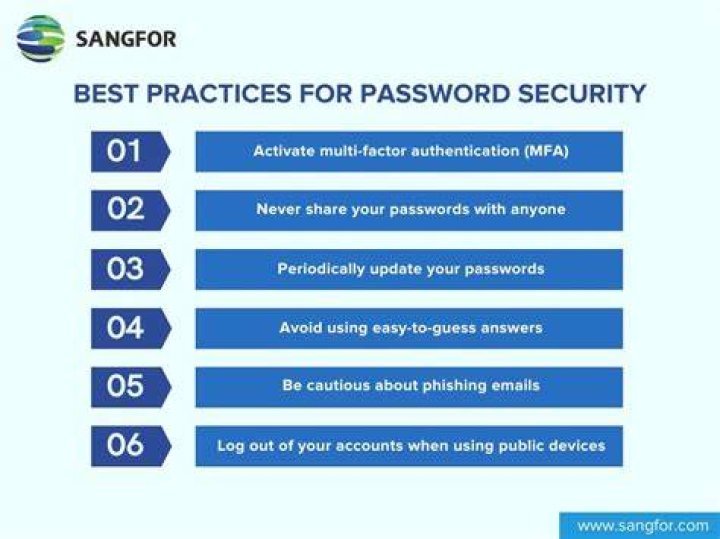
Secure Your Sessions: Sign Out on Shared Devices and Use Lock Screen Protections
Account security isn’t only about passwords. Session handling is where many people get surprised—especially on shared devices. If you use a family computer, workplace kiosk, or a friend’s phone, sign out after you watch. Even if you trust the device, assume it might later be accessed by others.
Also lock your device with a strong screen lock (PIN, pattern, or passcode) and enable auto-lock. When your device remains unlocked, anyone who picks it up could access your logged-in session. That can be as risky as a stolen password.
If your device supports biometric unlock, pair it with a secure device passcode fallback. Biometrics alone can be helpful, but your goal is to ensure a thief cannot easily bypass authentication.
Watch Out for Phishing: Learn the Common Social Engineering Patterns
Phishing is often effective because it targets emotions: urgency, curiosity, and fear. Common patterns include fake “account verification” messages, warnings about suspicious logins, or links to “resolve” an issue. If a message claims your account will be disabled unless you act immediately, treat it as suspicious.
Instead of clicking, open a new browser tab and navigate to the site directly or consult your bookmarks. Compare what the message asks you to do against what you know is normal for your account. Also verify the sender address carefully—fraudsters often use look-alike names.
Most importantly, never enter credentials into a page you arrived at from an email link or a messaging app. That simple habit blocks a large share of account takeovers.
Keep Your Email and Notifications Clean to Improve Detection
Your inbox is both a vulnerability and an early warning system. If attackers gain access to your email, they may reset your password and then take over your account. Therefore, secure your email with a strong password and 2FA, and monitor alerts from your email provider.
Turn on notifications for important security events when you can. Examples include “new sign-in,” “password changed,” or “recovery email updated.” These alerts let you react quickly—often faster than the attacker can complete the takeover.
At the same time, keep notification spam under control. Too many irrelevant alerts can cause “notification fatigue,” where you ignore the important ones.
Use Payment Safety Habits If You Ever Subscribe
If you pay for premium features or subscriptions, payment safety is part of legal and account safety. Avoid using shared payment methods on unknown devices, and never enter payment details on suspicious pages. When a payment flow looks unusual, stop and verify you’re on the correct, legitimate checkout.
If your platform supports it, consider privacy-preserving payment options such as virtual cards or merchant-controlled billing. These can help limit exposure if a payment credential is compromised.
Finally, review your billing statements regularly. Catching incorrect charges early reduces the damage and increases your ability to dispute charges before more funds are lost.
Know the Legal-Safety Boundary: Stay Informed About Your Viewing Context
“Legal safety” is not a single technical setting—it depends on local regulations and the way content is provided. While you can strengthen privacy and account security through best practices, you should also be mindful of how content availability relates to licensing in your region.
When using any streaming site, avoid downloading or redistributing content in ways that may violate local laws or platform terms. If your goal is personal viewing, focus on safe, legitimate playback methods rather than extensions, downloads, or file-sharing behaviors that can create legal exposure.
If you’re unsure about the legality of specific content categories in your area, consult local legal resources or official guidance. Security best practices help you reduce risk, but they can’t replace compliance with applicable rules.
Build a Simple Security Routine You Can Stick To
The best security changes are the ones you repeat. A short weekly or monthly routine can prevent many incidents. For example: check 2FA status, review logged-in devices, update passwords if needed, and verify email security settings.
Also make sure your recovery codes are stored somewhere safe and offline. If you ever lose access to your phone or authenticator app, having recovery codes ready can prevent panic-driven decisions that attackers exploit.
Lastly, keep your browser and operating system updated. Many attacks rely on known vulnerabilities, and updates are often the difference between “annoying” and “devastating.”
Why kissasian Security Habits Matter Beyond One Account
When people use kissasian with stronger privacy habits, they also tend to improve security across their entire digital routine. For instance, using a password manager, enabling 2FA, and reducing tracking are behaviors that protect many accounts—not just one streaming profile.
Think of it as building a consistent baseline: better device hygiene, safer browsing decisions, and fewer opportunities for credential theft. That’s how you stay in control while enjoying entertainment online.
Final Thoughts
Privacy, legal safety, and account security are best handled as a system, not as a one-time fix. Strengthen your credentials with unique passwords and 2FA, reduce tracking signals, verify links before logging in, and keep your device clean from malware risk. When you apply these best practices to kissasian usage, you create a safer experience that’s easier to maintain.
Sources [US-CERT (CISA) - Stop Think Fraud: Phishing and Security Guidance](https://www.cisa.gov/stopthinkconnect) [NIST - Digital Identity Guidelines (Authentication and Recovery Concepts)](https://pages.nist.gov/800-63-3/) [FTC - Consumer Advice on Online Security and Phishing](https://www.consumer.ftc.gov/) [OWASP - Authentication and Session Security Guidance](https://owasp.org/) [Mozilla Support - Reduce Tracking and Improve Privacy](https://support.mozilla.org/)
Keep Learning
