Security and privacy issues rarely start with something dramatic. More often, they begin with small decisions: using the same password everywhere, leaving permissions broad, clicking a link without checking it, or sharing data “just this once.” The good news is that you can prevent a surprising amount of risk with a focused, repeatable routine.
This supporting guide focuses on one long-tail need within the broader topic of digital safety: best practices for safe day to day security and privacy use. It is designed to help you reduce common threats like account takeovers, phishing, data leakage, and unwanted tracking. Along the way, you will see where sfix can fit naturally as a practical support for safer habits.
Build a Password and Account Setup That Attacks the Biggest Risk First
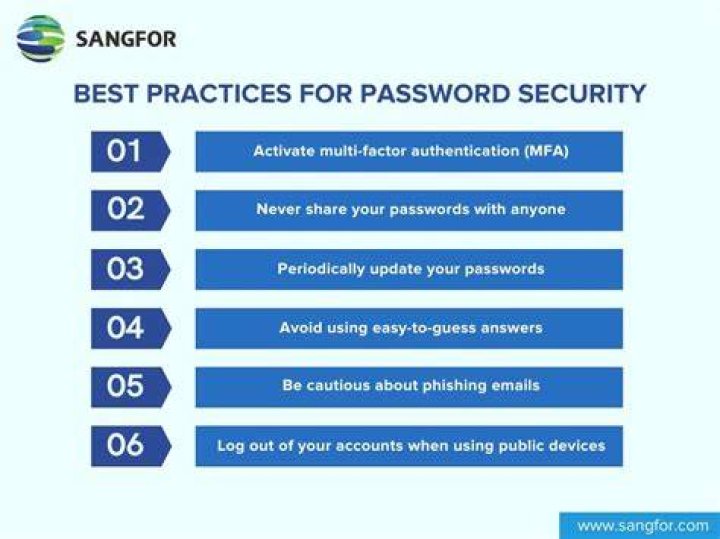
If you do only one thing for security, make it harder to access your accounts. Attackers frequently start with password reuse and credential stuffing, where leaked username and password pairs are tried across many services. Instead of relying on memory, use a password manager and unique passwords for every login.
Next, prioritize multi-factor authentication. In practice, “more factors” matter only if the factor is resilient to phishing and takeover attempts. Authenticator apps or security keys generally provide stronger protection than SMS because they are less vulnerable to SIM swapping and real time interception.
Finally, review account recovery settings. Many breaches persist even after you change your password because recovery methods still point to the same email, phone number, or security question that an attacker targeted. Update recovery contact details, remove unknown authorized devices, and verify that your email account is also protected with multi-factor authentication.
Practical checklist:
- Use a password manager to generate and store unique passwords.
- Enable multi-factor authentication on email, banking, and social accounts.
- Prefer authenticator apps or security keys over SMS when available.
- Audit recovery email, phone, and authorized devices.
- Check for suspicious login activity and set up alerts.
Spot Phishing and Deceptive Messaging Before It Reaches Your Accounts
Phishing success often depends on speed and urgency. Messages like “Your account will be closed today” or “Confirm your password immediately” aim to reduce your ability to verify. A strong defense is to slow down on purpose: do not act from the message alone, and do not log in through a link you did not request.
Instead, verify using a trusted path. For example, open a new browser tab and navigate to the service by typing the domain or using a bookmarked official page. Then check whether the warning is real inside your account. If it is legitimate, the service will show the issue there as well.
Also, pay attention to the message structure. Poor grammar, unusual sender addresses, unexpected attachments, and links that do not match the domain you expect are common indicators. However, attackers can improve their formatting, so technical verification is still important even when the message looks “professional.”
If you use sfix as part of your safety workflow, treat it as a support for verification and consistency. The key idea is to reduce the number of times you make a judgment call under pressure.
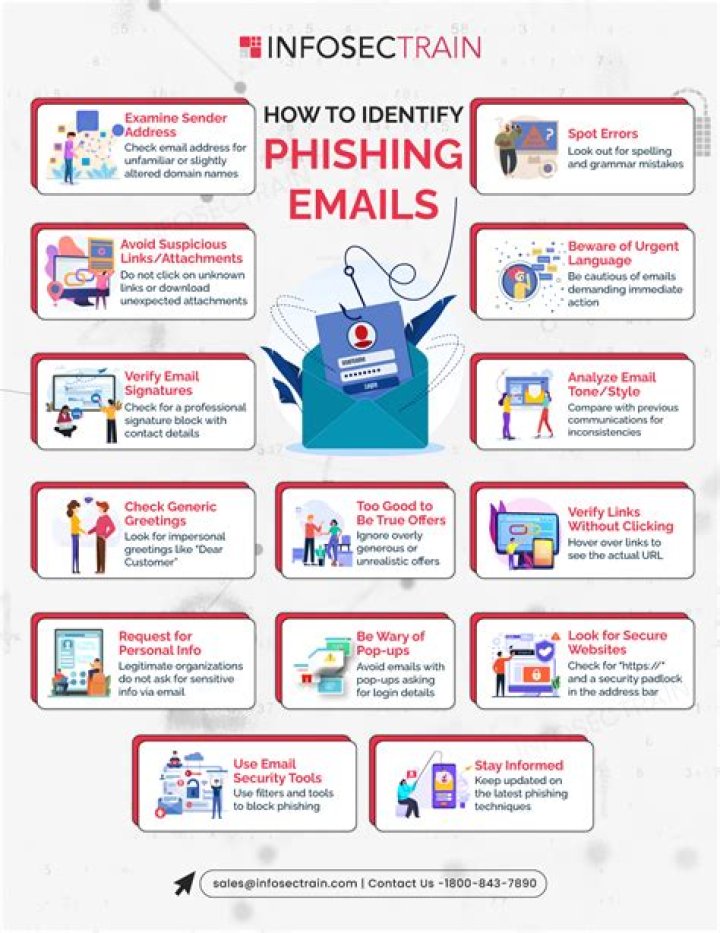
Quick verification habit: When a message asks you to log in or pay immediately, pause, confirm the domain, and open the site directly yourself. This single routine blocks many phishing attempts.
Lock Down Device Security So Attacks Can Escape Less Easily
Even with strong passwords, malware and compromised devices can expose your data. If your computer or phone is infected, attackers can capture keystrokes, steal session tokens, or access saved credentials. Device hardening is the difference between “secure accounts” and “secure outcomes.”
Start with updates. Operating system patches and browser updates fix known vulnerabilities that attackers already know how to exploit. Enable automatic updates when possible so security fixes do not depend on your memory.
Next, reduce app risk. Only install software from reputable sources, and review permissions after installation. If an app requests broad access like contacts, notifications, or microphone without a clear reason, it increases privacy exposure. Remove apps you do not use and revoke permissions you no longer need.
Finally, consider secure browser and operating system settings. Use a modern browser with built-in phishing protection, disable unnecessary extensions, and remove extensions you cannot explain. Extensions can become a privacy risk because they may read page content or track activity.

What to do this week:
- Turn on automatic OS and browser updates.
- Remove unknown browser extensions.
- Review app permissions for location, microphone, camera, contacts.
- Uninstall unused apps and check for suspicious ones.
- Use a screen lock and enable device encryption if supported.
Reduce Tracking and Limit Data Exposure in Everyday Browsing
Privacy risk is often the sum of many data collection points, not one single breach. Websites, apps, ad networks, and analytics providers can build profiles based on your browsing behavior. Even if you never “give” your data directly, tracking can infer interests, identity signals, and device characteristics.
Start by tightening browser privacy controls. Use tracking protection features, disable third-party cookies when feasible, and review permissions for location, notifications, and camera access. Manage site permissions regularly; many users grant access once and forget it.
Next, be intentional about account data sharing. Many services ask for permission to “improve recommendations” or “personalize experiences.” Personalization is not inherently harmful, but you should decide what data you want to trade for convenience. When possible, choose settings that minimize data sharing while still meeting your goals.
Also, understand what you are signing up for. When a form requires optional fields, ask whether those fields genuinely improve your service experience. If you do not need it, avoid giving extra data.
For users who want a consistent way to manage safer browsing behaviors, sfix can be a useful companion—especially when you want a practical process rather than scattered reminders.
Privacy wins that usually require little effort:
- Enable tracking protection and block third-party cookies.
- Review site permissions and remove unnecessary access.
- Limit data sharing options in account settings.
- Use separate profiles or browsers for sensitive activities when appropriate.
Control Sharing and Permissions in Apps, Social Accounts, and Cloud Services
Many privacy issues come from over-permission and broad sharing. When an app can access your contacts, photos, location, or messages, it increases the surface area for exposure and misuse. Permissions are not “set and forget”—they should match what you need today.
Review social media privacy settings regularly. Default visibility changes across platforms over time, and some settings are easy to overlook. Check who can see your posts, who can find you via email or phone, and whether your location is exposed in posts or stories.
In cloud services, verify sharing links and folder permissions. Public links and “anyone with the link” access are convenient, but they can persist longer than you expect. If you share files, use the least permissive option and revoke access when the collaboration is done.
Finally, watch for third-party integrations. Social platforms and productivity tools often let external apps connect to your account. Remove integrations you do not recognize, and avoid granting broad permissions to new apps unless you trust the provider and purpose.
Permission audit method:
- List apps with sensitive permissions (camera, microphone, location, contacts).
- Decide whether you need them for the specific task you use the app for.
- Revoke permissions that you do not need.
- Remove social integrations and check connected apps.
- For cloud shares, use explicit recipients rather than public links when possible.
Use Safer Wi Fi and Network Habits Without Overcomplicating
Public networks are a common privacy concern and a frequent entry point for attacks. You cannot assume that Wi Fi in airports, cafes, or coworking spaces is safe. The risk depends on network configuration, encryption, and how attackers target devices on the same network.
Start with basics: avoid logging into sensitive accounts while on unfamiliar public Wi Fi unless you use an encrypted connection. Modern browsers and secure sites use encryption in transit, but it is still smart to add protection when the environment is uncertain.
If you use a VPN for sensitive browsing, choose reputable services and confirm that the VPN is functioning before you enter credentials. Also, disable file sharing and enable firewall settings on your device. These steps reduce how easily other devices can discover or interact with yours.
Finally, be careful with “free Wi Fi” portal pages. Attackers can create fake networks with similar names to trick users into entering credentials. Verify the network name and, when possible, prefer networks that require authentication through a trusted provider.
sfix can complement this by helping you keep your security habits consistent across environments, so you are not relying on memory when you are out and about.
- Avoid sensitive logins on unknown public Wi Fi.
- Prefer encrypted connections and consider a VPN for added protection.
- Keep device firewalls enabled and disable unnecessary sharing.
- Verify Wi Fi network names before connecting.
Plan for Recovery: What to Do If Something Goes Wrong
Even with best practices, incidents can happen. A strong privacy and security posture includes a recovery plan, so you can act quickly instead of searching for steps while stressed.
First, know your escalation path. If you suspect credential compromise, change the password immediately for the affected account and any other accounts that use the same password. Then check your account for session activity and revoke unknown sessions.
Second, check email security. Many attackers try to reset passwords via compromised email accounts. If you regain control, protect your email first with multi-factor authentication, review recovery settings, and watch for forwarding rules.
Third, monitor for phishing and fraud activity. Look for new logins, password reset emails you did not request, and suspicious changes to profile information. If financial accounts are involved, contact the financial institution quickly to prevent further damage.
When you build your routines around verification and account review, recovery becomes more manageable. sfix fits well into that mindset by encouraging safer workflows you can repeat.
Recovery quick steps:
- Change passwords for compromised accounts and any reused credentials.
- Revoke active sessions and remove unknown devices.
- Secure email with multi-factor authentication and review recovery settings.
- Check forwarding rules, filters, and mailbox access.
- Contact support for critical services if needed.
Final Thoughts
Safe security and privacy use is not about perfect behavior. It is about reducing high-impact risks first—strong account protection, careful verification against phishing, device hardening, and tighter privacy permissions. If you want a practical way to support those habits over time, sfix can be a helpful complement to your day to day routine.
When you combine these best practices with regular reviews, you lower the odds of account takeover and make your personal data harder to collect and misuse. Start small, repeat often, and let consistency do the heavy lifting.
