Streaming should feel effortless—until you think about how many accounts, devices, and networks touch your activity. Security and privacy matter because a single weak password, a reused login, or a careless setting can expose your identity, viewing habits, and personal data.
This supporting guide focuses on one practical problem: keeping your streamcloud experience safe through stronger account protection and safer streaming habits. You will learn what to change, what to verify, and how to build a routine that lowers risk without slowing you down.
Start with the account threats that actually impact streaming users
Most streaming security issues come from predictable sources: account takeover, credential stuffing, phishing, and device compromise. Even if you only use streaming services, attackers often target the same “unlocked” habits—password reuse, missing multi-factor authentication, and clicks that should not happen.
Account takeover is especially common because stolen credentials can be tested quickly across many services. If your email is compromised or your password is reused, your streaming accounts become the next logical target. Meanwhile, privacy risk can come from trackers, ad personalization, and network-level monitoring.
To protect streamcloud effectively, treat your streaming account like any other high-value login: protect the credential, reduce the chance of deception, and limit what can be inferred from your activity.
Lock down your login with multi factor authentication and unique passwords
The highest impact change for most users is enabling multi-factor authentication (MFA). MFA adds a second checkpoint, so even if a password leaks, the attacker still faces friction. Choose an MFA method that you will actually use consistently, and make sure your recovery options are correct.
Next, stop reusing passwords. Credential stuffing attacks rely on leaked username and password pairs from other breaches. When your streaming password matches another site, the attacker does not need to “break” anything—they simply test stolen credentials.
Use a password manager to generate and store unique passwords for every service, including email. Then verify that your email account itself is protected with MFA, because email controls the reset flow for many accounts. With streamcloud, the goal is straightforward: reduce account takeover probability to as close to zero as practical.
Quick checklist you can complete in one sitting
- Enable MFA on your streamcloud account
- Use a unique, randomly generated password for streamcloud
- Secure your email with MFA and updated recovery methods
- Review active sessions and sign out from devices you do not recognize
- Confirm your profile email and phone number are correct
Harden your email and recovery path to prevent account resets
Email is the key that unlocks password resets. If your inbox is weak, attackers can take over your streaming account even if you enabled MFA on the streaming service. That is why recovery protection should be treated as part of your streaming security plan, not as an afterthought.
Look for suspicious login alerts, unusual forwarding rules, or filters that could hide messages. Many providers also show security activity such as recent sign-ins and device changes. If something looks off, address it immediately before an attacker uses the reset link.
Also protect your recovery methods from being easily redirected. If your phone number or recovery email can be changed without extra checks, an attacker who gets that access can bypass your protections. The safest approach is to ensure that any account recovery changes also require MFA and that you control the underlying identity.
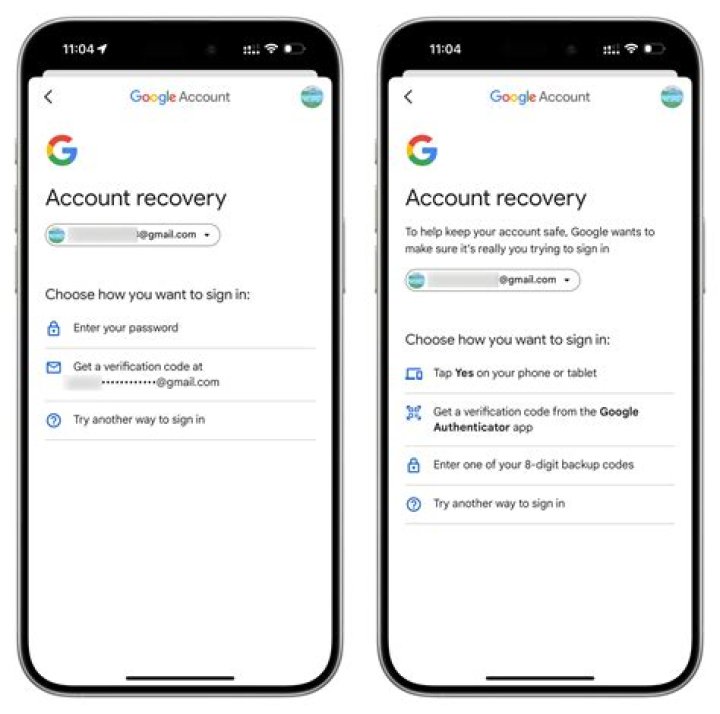
For streamcloud users, securing the recovery path typically delivers faster results than chasing obscure settings. When your email is trustworthy, the rest of your streaming account becomes much harder to hijack.
Defend against phishing and “login” scams using safe verification habits
Phishing is not usually complicated—it is persuasive. Attackers send messages that imitate trusted brands, then direct you to a fake sign-in page. The most dangerous part is that many phishing attempts look legitimate enough to bypass quick skepticism, especially on mobile.
Adopt a safe verification routine: do not sign in from links in unsolicited messages. Instead, open a new browser tab, navigate directly to the official service site, and log in only when you arrive there intentionally. For streamcloud, the same principle applies regardless of where the scam appears.
Also be careful with “support” offers that ask for your credentials. Real support teams do not need your password to help you. If you ever see a message requesting credentials, stop and report it using the platform’s tools or your email provider’s abuse flow.
Spot the most common phishing cues
- Unexpected urgency or threat language
- Requests to verify credentials immediately
- Generic greetings or mismatched branding
- Links that do not match the expected domain
- Offers that ask you to install “security updates”
When you train yourself to verify manually, you reduce the chance that a clever message becomes account access.
Manage device security so your streaming sessions do not become entry points
Even strong account credentials can be undermined by malware, risky browser extensions, or compromised devices. Many streaming users install helpful tools—then forget that some extensions request broad permissions. If a malicious extension can read cookies or tamper with navigation, it may capture session data.
To improve safety, review installed browser extensions and remove anything you do not recognize. Keep your operating system and browser up to date, because security patches address known vulnerabilities that attackers actively exploit. On phones and tablets, enable screen locks and keep your apps updated through official app stores.
Finally, watch your shared-device habits. If you stream on public or shared computers, use guest profiles and sign out fully afterward. Session tokens can persist longer than you expect, which can lead to unauthorized access if someone else returns to the page later.
Reduce privacy exposure by controlling tracking and limiting sensitive sharing
Security and privacy often overlap, but privacy protection includes more than login safety. Streaming platforms can infer preferences from watch history, device identifiers, and interactions like search terms and playback behavior. That does not automatically mean you are in danger, but it can create a profile about you that you may not want to share.
Start by reviewing privacy-related settings: playback personalization, ad personalization, and marketing communications. If streamcloud offers options to limit tracking or tailor recommendations, choose the strictest setting that still gives you a comfortable experience.
Then consider network privacy. If you regularly stream on shared Wi-Fi, avoid logging in to your account on insecure networks. Instead, prefer trusted networks and consider using privacy protections that reduce network-level visibility while you stream.
Practical privacy actions you can take without losing convenience
- Disable ad personalization where available
- Limit marketing emails and data sharing preferences
- Use secure Wi-Fi networks when signing in
- Clear sensitive browsing data if you use shared devices
- Review device identifiers and sign-out on old devices
Spot account issues early with session review and security alerts
Account takeover rarely announces itself politely. Instead, you may notice subtle signs: login alerts you did not trigger, unexpected device activity, or changes to your email address. Many platforms also provide security dashboards where you can view recent logins, active sessions, and connected devices.
Make this a routine habit. Once a week—or at least monthly—check for new sessions and sign out of anything you do not recognize. If you see suspicious activity, change your password immediately and review any connected recovery methods.
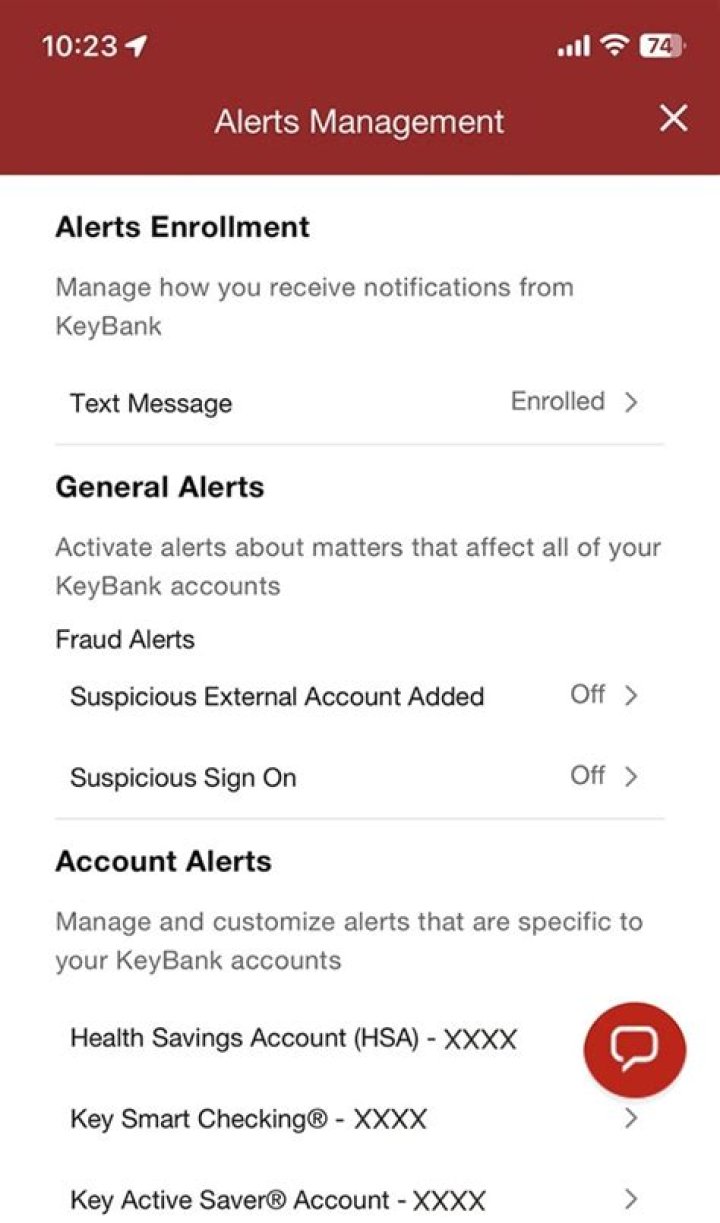
In addition, enable security notifications so you hear about changes quickly. Alerts help you respond before an attacker finishes takeover steps. For streamcloud users, early intervention is the difference between “locked out” and “account recovered quickly.”
Create a simple incident response plan if you think your account is compromised
Even with good habits, no one is immune. If you suspect compromise, the best approach is structured and fast. The main objective is to stop ongoing access, then reduce the attacker’s ability to maintain control.
First, sign out of all devices. Then change your password to a unique one that you have not used elsewhere. After that, review your email and recovery settings—attackers commonly aim to change the recovery path so they can regain access later.
Finally, check your devices for signs of compromise. If you installed a suspicious extension or clicked an unknown download prompt, remove it and run security scans. For streamcloud, acting quickly protects not only your current viewing session but also future sign-ins.
Incident steps in order
- Sign out of all active sessions
- Change your password immediately
- Secure your email account and confirm recovery settings
- Review profile changes and connected devices
- Remove suspicious extensions and scan devices
- Contact support if available to regain full control
Final Thoughts
Safe streaming is less about fear and more about good defaults: unique passwords, MFA, careful recovery protection, and a habit of checking sessions and alerts. When you pair those practices with privacy-aware settings, your streamcloud account becomes significantly harder to hijack and easier to trust. Build the routine once, then let your future self benefit every time you press play.
Keep Learning
