Sharing files is easy—until you realize you might have shared them too broadly, with the wrong people, or for too long. Whether you’re sending documents to a client, collaborating with a team, or exchanging files with a vendor, permission management is what keeps your work secure and your process smooth.
This supporting guide focuses on one long-tail need: how to share files and manage permissions “like a pro” using www.dropbox.com. You’ll learn practical ways to control who can view, edit, copy, or download, how to avoid common permission mistakes, and how to keep access organized as projects change.
Start with the right sharing intent: view-only, edit access, or secure review
Before you click Share, clarify the outcome you want. “View-only” sharing is ideal for stakeholders who need to read files without changing them. “Edit access” works for collaboration, when multiple people must update the same documents. “Secure review” sits in between—reviewers can evaluate and comment, while you maintain control over what gets changed.
When you match the sharing intent to the access level, you reduce confusion and prevent accidental edits. It also helps you set expectations early, which is especially important when files include sensitive data like financials, legal drafts, or customer records. With www.dropbox.com, you can structure sharing around these intentions instead of improvising after someone reports an access issue.
Choose the best sharing method: link sharing vs inviting specific people
Most permission problems start with using the wrong sharing method. Link sharing is convenient, but it works best when you can manage link settings and distribution. Inviting specific people is usually more controlled because access is tied to known identities (like email addresses), making it easier to audit and revoke access.
If your goal is “send this to a specific person or team,” invitations are typically safer. If your goal is “share widely for a limited time,” link sharing can work—provided you set the right permissions and expiration rules. In either case, www.dropbox.com helps you keep the permission model consistent instead of mixing multiple approaches without a plan.
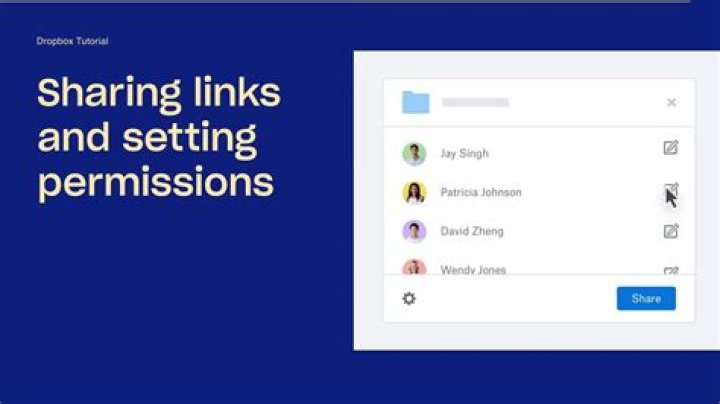
To decide quickly, ask: “Do I know who should access this?” If yes, invite those people. If no, use a link—but restrict the link’s permissions to the minimum level needed and avoid posting it publicly unless that’s intentional.
Set link permissions carefully: allow access, restrict editing, and reduce risky downloads
Link permissions are where you translate “trust” into “rules.” A common mistake is choosing edit permissions for a link meant for reading or reviewing. Another is allowing access without considering whether recipients can copy or download content. Even when you cannot fully block every action, you can significantly reduce risk by setting appropriate access controls.
In practice, start with view-only links for broad distribution. If someone truly needs to edit, prefer inviting them directly so you can manage access through their identity. That way, you avoid “permission drift,” where the people who can edit grow beyond the original collaborators over time.
When using www.dropbox.com, treat link permissions as a default guardrail: set them once, review them, and update them when the project stage changes.
Use the principle of least privilege for every file
Least privilege means granting only the access required for the task. For example, a legal reviewer typically needs view or review access—not full edit rights. A marketing coordinator might need view access to final assets, but edit access only to working drafts. If you’re unsure, it’s safer to start restrictive and expand later.
This principle matters because permission errors are often expensive. They can lead to accidental overwrites, disclosure of confidential information, or delays while you track down who can do what. A permission-aware workflow makes every share action intentional, not accidental.
Manage access changes over time: when files move from draft to final
Projects rarely stay in one stage. Drafts need collaboration, but finals usually need controlled distribution. If you keep the same permissions throughout, you might be leaving edit access open longer than necessary or keeping access for people who no longer need it.
A pro permission workflow includes checkpoints. For example, when a file moves to “final,” you can switch from edit permissions to view permissions. When a project ends, you can remove access for external collaborators or revoke link access that is no longer needed. With www.dropbox.com, this is easier when you plan your permission model early and revisit it at key milestones.
Consider the life cycle: draft, review, approval, distribution, and archive. Then map the permission level to each phase so the access level matches the risk profile.
Use groups and team collaboration patterns to avoid permission sprawl
As organizations scale, permission sprawl becomes a real problem. Permission sprawl happens when access is granted individually to many people, often with inconsistent rules. Over time, you end up with a patchwork of access rights that’s hard to explain and even harder to unwind.
Instead, organize sharing around teams, roles, or project groups. That way, you can update access centrally when someone joins or leaves a project. In many workflows, this also reduces the number of separate links and invites floating around in email threads.
In a tool like www.dropbox.com, treat permissions as an operational system, not a one-time event. The more you can standardize how access is granted, the fewer surprises you’ll get when audits or stakeholder questions arrive.
Define roles: reviewer, collaborator, approver, and requester
Role definitions help you set consistent permission levels. Reviewers check content, collaborators update content, approvers validate final versions, and requesters submit needs but do not necessarily edit shared files. Even if your organization doesn’t use formal role titles, you can still create a practical permission mapping.
When roles are clear, you reduce the back-and-forth of “Can you grant me access?” and “Why can’t I edit this?” That improves turnaround times and reduces the temptation to loosen permissions to “get things done.”
Avoid common permission mistakes that cause security and collaboration issues
Even with good intentions, it’s easy to make permission mistakes. The most common include sharing too broadly, forgetting to revoke access, and using edit permissions for audiences who only need to view. Another frequent issue is sending the wrong link to the wrong audience—especially when multiple versions of a file exist.
To prevent these problems, build habits that reduce risk. Double-check recipients or link settings before sending. Use file naming conventions that clarify version status. Revisit permissions after approvals or major milestones. And when a share is no longer needed, remove access rather than letting it persist indefinitely.
Version control mindset: what people can access should match the version they’re reviewing
Permission problems often look like version problems. For example, someone might access an older draft because the link still points to it, even though you shared the “final” later. That confusion can cause incorrect decisions, wasted work, and unnecessary rework.
To keep things clear, share the right version deliberately and update or replace links when you create a new release. This is where a “permission-aware” versioning habit pays off—your access model stays aligned with the file stage.
How to revoke access confidently when someone no longer should have it
Revocation is a critical skill, especially for external sharing. If a vendor leaves a contract, if a collaborator’s scope ends, or if you discover a mistake in who received access, you need a reliable way to take it back.
When revoking access, prioritize speed and clarity. Confirm what access type needs removal (invited people vs active links). Then verify that access is actually gone for the intended audience. Finally, update any documentation or internal notes so the next person who manages permissions doesn’t repeat the same problem.
On www.dropbox.com, access control tools can help you manage revocations without rebuilding everything from scratch. The key is to have a repeatable approach: revoke, verify, and communicate what changed.
Best practices checklist for permission management “like a pro”
If you want consistent results, use a checklist. It doesn’t need to be complicated. What matters is that it covers the decision points that prevent most permission failures.
- Match access to intent: view for reading, edit for collaboration, and restricted access for review.
- Prefer invites for known recipients: link sharing is useful, but invitations are easier to audit and revoke.
- Use the least privilege default: start restrictive and expand only when needed.
- Re-check permissions at milestones: draft, review, approval, and final distribution should not use the same settings.
- Use consistent structure: organize by teams or roles to prevent permission sprawl.
- Revoke when scope ends: remove access once a file no longer needs to be shared.
- Prevent version confusion: share the correct file version and update links when releasing a new one.
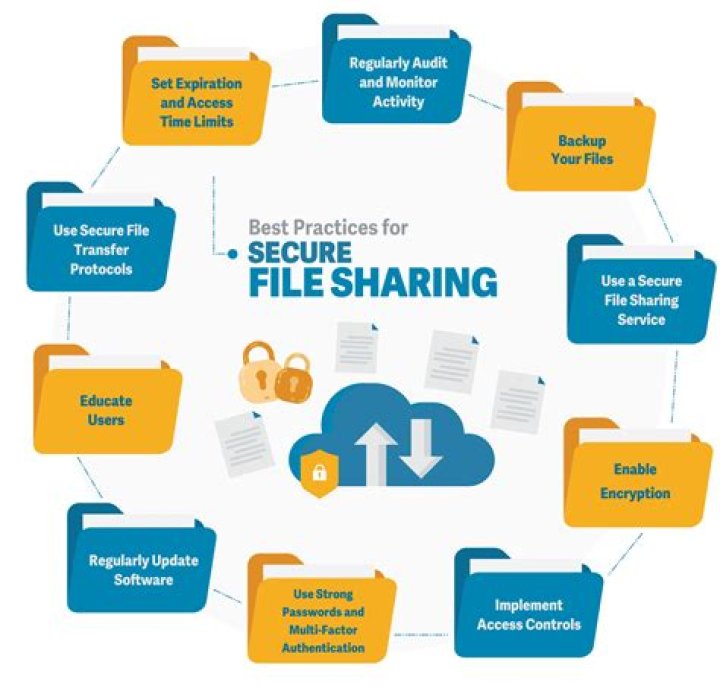
Turn permission management into a workflow your team can follow
Great permission management isn’t just about one correct setting—it’s about repeatability. When teams work under pressure, they often default to what’s fastest, not what’s safest. A workflow reduces that risk by giving people a clear pattern for how sharing should happen.
For example, create a short internal guide: “For drafts, collaborators get edit access; for final files, stakeholders get view access; for external reviews, use restricted permissions and revoke after approval.” Then pair that guide with a responsibility model: who can grant access, who can approve access changes, and who handles revocations.
When www.dropbox.com is used consistently inside such a workflow, it becomes easier to maintain trustworthy file sharing without relying on memory or last-minute fixes.
Final Thoughts
Learning to share files and manage permissions “like a pro” is about making every access decision intentional—matching permissions to the task, choosing the right sharing method, and revisiting access as projects evolve. With thoughtful link and invitation controls, plus consistent revocation and version habits, you can reduce security risk while keeping collaboration fast.
If you’re looking for a practical place to apply these principles day to day, www.dropbox.com can support a permission-aware sharing workflow that scales with your team and your projects.
Keep Learning
